


A newly disclosed Windows 11 security vulnerability called FastUnlock allows someone with physical access to a locked PC to execute programs without entering the user’s password or PIN. Security researcher Nightmare Eclipse publicly disclosed the flaw on November 19, 2026, and cybersecurity company ThreatLocker independently reproduced the technique on the same day.
The vulnerability exploits Microsoft’s built-in Narrator accessibility feature during the account recovery process. It can work on BitLocker-encrypted systems, including Windows 11 installations with November 2026 security updates. However, the demonstrated attack has important limitations, and it does not establish that attackers can automatically gain administrator privileges or access every file on a locked computer.
The researcher, who also uses the name MSNightmare, published technical details and a demonstration through the FastUnlock GitHub repository. The disclosure identifies Windows 11 26H2 as an affected version, although other Windows releases have not been conclusively tested.
The attack takes advantage of how Narrator handles interface elements while Windows is displaying the sign-in screen. When the Microsoft account recovery interface is active, Narrator can interact with a background window that should not be accessible in this context. That interaction can expose Windows Settings and eventually provide a route to launching other programs.
Nightmare Eclipse attributes the behavior to missing restrictions in Narrator’s updated interface. The researcher claims the technique worked consistently across tested machines, including one running Windows 11 26H2 with November security patches installed.
ThreatLocker researchers Kenneth Walker and William Pires subsequently examined the vulnerability and confirmed that an executable could be launched from an external drive without authenticating to a regular Windows account.
Crucially, ThreatLocker’s demonstration executed code under the restricted WSIAccount identity associated with the Windows sign-in environment. This is not an administrator account, and the testing did not demonstrate full control of the existing user’s session.
The distinction matters because running a program at the lock screen is not necessarily equivalent to obtaining unrestricted access to a Windows installation. Further exploitation might be possible, but broader access to personal data or administrative functions has not been established by the published proof of concept.
The attack also has specific prerequisites. An attacker must physically access the computer, and at least one account must be linked to a Microsoft account accessible through the recovery interface. It is not a remotely exploitable vulnerability based on the currently demonstrated technique.
FastUnlock is particularly relevant to gaming laptops and portable Windows PCs that may be left unattended in public or shared environments. A locked screen alone cannot be assumed to prevent the demonstrated execution of programs when the required conditions are present.
BitLocker encryption does not automatically stop this attack because the technique targets a running Windows environment rather than directly breaking the encryption protecting the storage drive.
On systems configured with TPM-only BitLocker protection, Windows can unlock the operating system drive automatically during startup after verifying the system’s integrity. By the time the Windows sign-in screen appears, the operating system already has access to the encrypted volume.
FastUnlock operates at that stage, taking advantage of the accessible Windows environment instead of recovering or cracking BitLocker encryption keys.
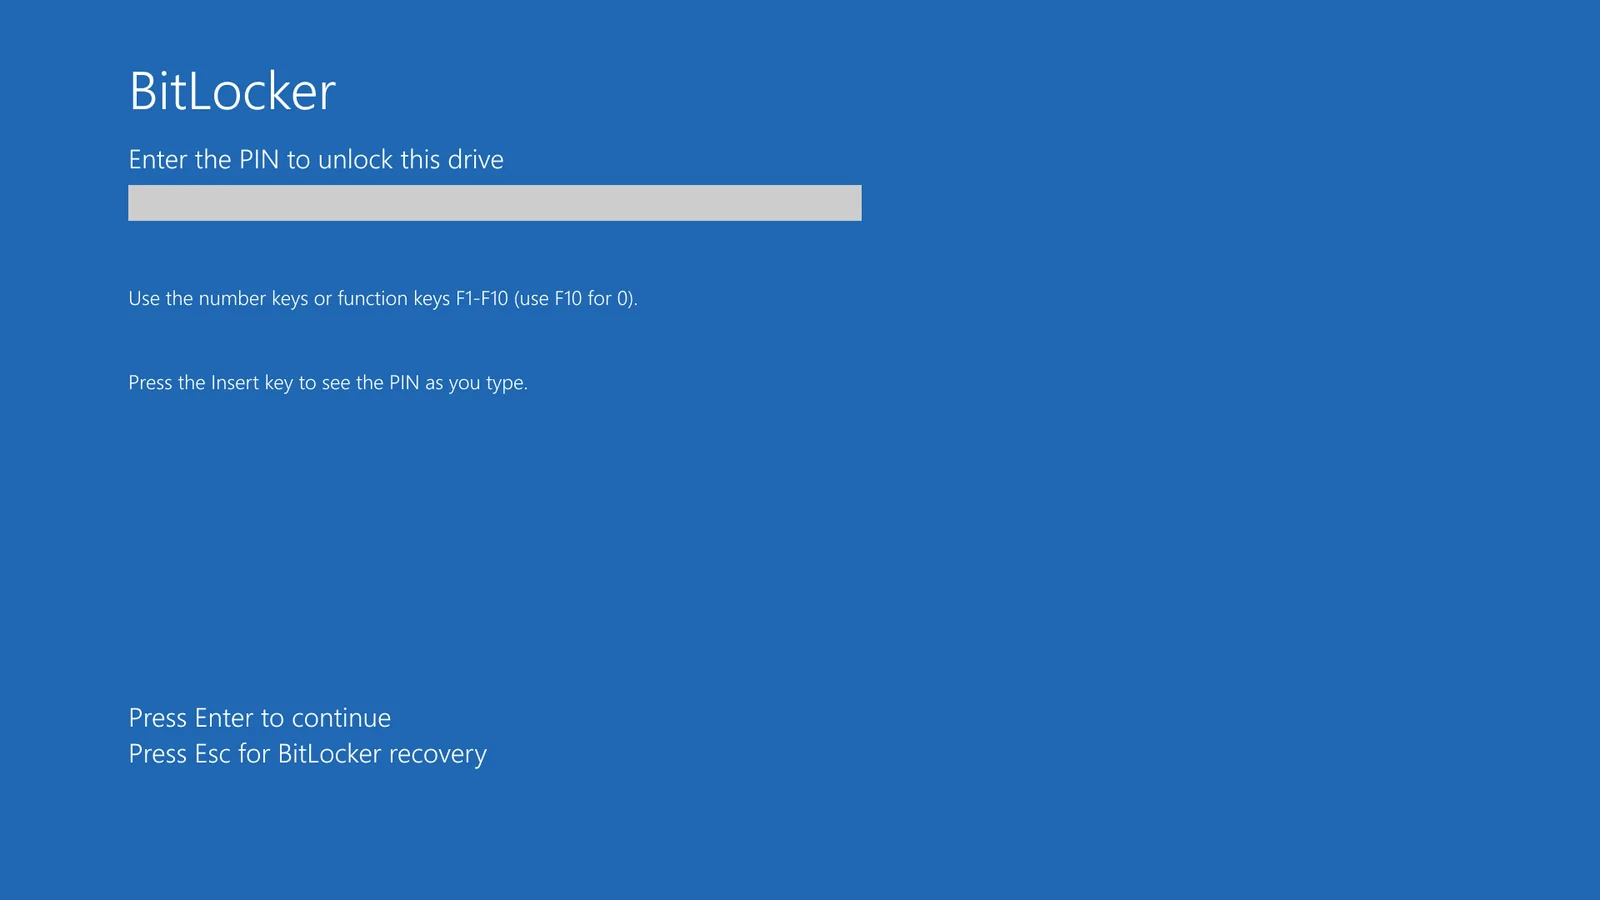
ThreatLocker recommends a BitLocker preboot PIN as a mitigation for computers that are powered off or hibernated. Unlike a Windows Hello sign-in PIN, the preboot PIN must be entered before the operating system drive can unlock and Windows can start.
Microsoft’s existing BitLocker security documentation similarly recommends TPM-plus-PIN protection and shutting down or hibernating devices when stronger physical security is required.
However, a preboot PIN does not prevent the demonstrated vulnerability on a computer that is already running and merely displaying its lock screen. It also does not provide the same protection when a device resumes from ordinary sleep without requiring preboot authentication.
The disclosure comes amid continuing changes to Windows security features, including the November 2026 expansion of Memory Integrity protection on eligible systems. Memory Integrity addresses a different class of security threats and has not been demonstrated to prevent FastUnlock.
As of the reviewed reporting, Microsoft has not confirmed a security update specifically addressing FastUnlock. There is also no established evidence in the published research that the vulnerability is being actively exploited in attacks outside controlled demonstrations.
Until a fix becomes available, users concerned about physical access to their Windows 11 PCs can reduce exposure by keeping devices under their control and using shutdown or hibernation alongside BitLocker preboot authentication where supported. Simply locking an already running computer does not eliminate the demonstrated risk.
